AWS Security Blog

See yourself in cyber: Highlights from Cybersecurity Awareness Month
As Cybersecurity Awareness Month comes to a close, we want to share some of the work we’ve done and made available to you throughout October. Over the last four weeks, we have shared insights and resources aligned with this year’s theme—”See Yourself in Cyber”—to help advance awareness training, and inspire people to join the rapidly […]
How to control non-HTTP and non-HTTPS traffic to a DNS domain with AWS Network Firewall and AWS Lambda
December 7, 2022: We added a caveat to the solution, for those using a traffic steering mechanism, in this post. Security and network administrators can control outbound access from a virtual private cloud (VPC) to specific destinations by using a service like AWS Network Firewall. You can use stateful rule groups to control outbound access […]

Export historical Security Hub findings to an S3 bucket to enable complex analytics
AWS Security Hub is a cloud security posture management service that you can use to perform security best practice checks, aggregate alerts, and automate remediation. Security Hub has out-of-the-box integrations with many AWS services and over 60 partner products. Security Hub centralizes findings across your AWS accounts and supported AWS Regions into a single delegated […]

AWS successfully renews GSMA security certification for US East (Ohio) and Europe (Paris) Regions
Amazon Web Services is pleased to announce that our US East (Ohio) and Europe (Paris) Regions have been re-certified through October 2023 by the GSM Association (GSMA) under its Security Accreditation Scheme Subscription Management (SAS-SM) with scope Data Centre Operations and Management (DCOM). The US East (Ohio) and Europe (Paris) Regions first obtained GSMA certification […]

New AWS whitepaper: Using AWS in the Context of Canada’s Controlled Goods Program (CGP)
Amazon Web Services (AWS) has released a new whitepaper to help Canadian defense and security customers accelerate their use of the AWS Cloud. The new guide, Using AWS in the Context of Canada’s Controlled Goods Program (CGP), continues our efforts to help AWS customers navigate the regulatory expectations of the Government of Canada’s Controlled Goods […]

Analyze Amazon Cognito advanced security intelligence to improve visibility and protection
January 28, 2025: The following blog post describes how to process AWS CloudTrail logs for user authentication events and query events for additional intelligence. Amazon Cognito added support for exporting threat protection user activity logs, which helps to streamline log processing for Plus feature tier customers. However, customers in the Plus tier can still use […]

Use IAM Access Analyzer policy generation to grant fine-grained permissions for your AWS CloudFormation service roles
AWS Identity and Access Management (IAM) Access Analyzer provides tools to simplify permissions management by making it simpler for you to set, verify, and refine permissions. One such tool is IAM Access Analyzer policy generation, which creates fine-grained policies based on your AWS CloudTrail access activity—for example, the actions you use with Amazon Elastic Compute […]
IAM Access Analyzer makes it simpler to author and validate role trust policies
AWS Identity and Access Management (IAM) Access Analyzer provides many tools to help you set, verify, and refine permissions. One part of IAM Access Analyzer—policy validation—helps you author secure and functional policies that grant the intended permissions. Now, I’m excited to announce that AWS has updated the IAM console experience for role trust policies to […]
Best practices for setting up Amazon Macie with AWS Organizations
In this post, we’ll walk through the best practices to implement before you enable Amazon Macie across all of your AWS accounts within AWS Organizations. Amazon Macie is a data classification and data protection service that uses machine learning and pattern matching to help secure your critical data in AWS. To do this, Macie first […]
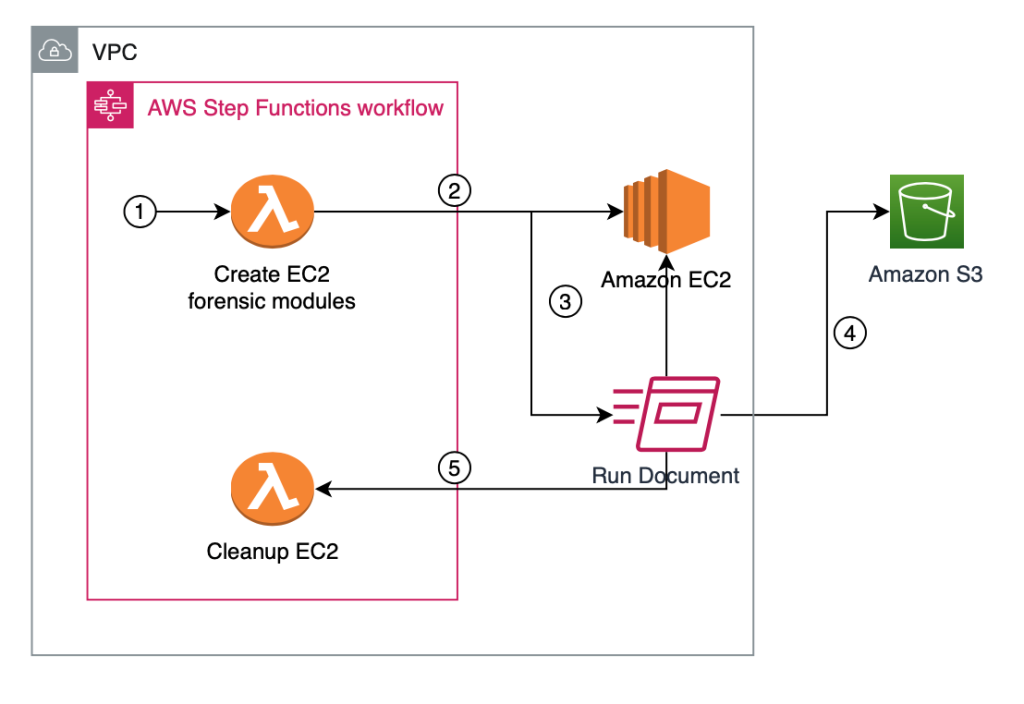
How to automatically build forensic kernel modules for Amazon Linux EC2 instances
In this blog post, we will walk you through the EC2 forensic module factory solution to deploy automation to build forensic kernel modules that are required for Amazon Elastic Compute Cloud (Amazon EC2) incident response automation. When an EC2 instance is suspected to have been compromised, it’s strongly recommended to investigate what happened to the […]