AWS Security Blog
Category: AWS WAF

Migrating your rules from AWS WAF Classic to the new AWS WAF
December 2, 2024: This post has been updated to reflect the transition to WAFV2, with aligned 1:1 mapping from Classic partner-managed rules to partner-managed rules. AWS WAF Classic support will end on September 30, 2025. In November 2019, Amazon launched a new version of AWS Web Application Firewall (WAF) that offers a richer and easier […]

How to use CI/CD to deploy and configure AWS security services with Terraform
Like the infrastructure your applications are built on, security infrastructure can be handled using infrastructure as code (IAC) and continuous integration/continuous deployment (CI/CD). In this post, I’ll show you how to build a CI/CD pipeline using AWS Developer Tools and HashiCorp’s Terraform platform as an IAC tool for AWS Web Application Firewall (WAF) deployments. AWS […]

Trimming AWS WAF logs with Amazon Kinesis Firehose transformations
In an earlier post, Enabling serverless security analytics using AWS WAF full logs, Amazon Athena, and Amazon QuickSight, published on March 28, 2019, the authors showed you how to stream WAF logs with Amazon Kinesis Firehose for visualization using QuickSight. This approach used no filtering of the logs so that you could visualize the full […]

How to analyze AWS WAF logs using Amazon Elasticsearch Service
September 9, 2021: Amazon Elasticsearch Service has been renamed to Amazon OpenSearch Service. See details. Log analysis is essential for understanding the effectiveness of any security solution. It can be valuable for day-to-day troubleshooting and also for your long-term understanding of how your security environment is performing. AWS WAF is a web application firewall that […]
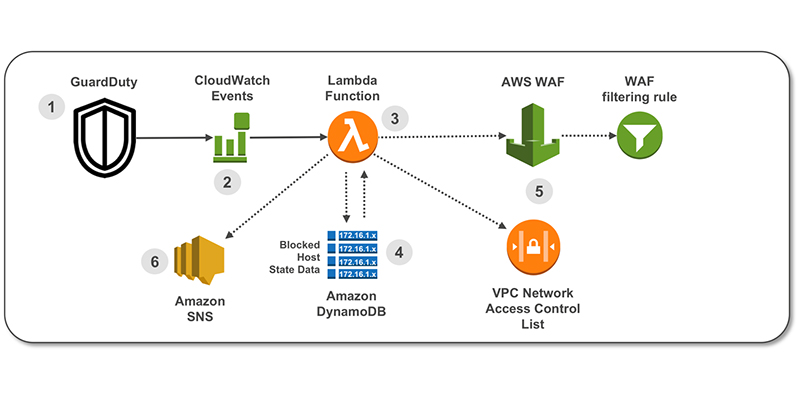
How to use Amazon GuardDuty and AWS Web Application Firewall to automatically block suspicious hosts
April 25, 2023: We’ve updated this blog post to include more security learning resources. When you’re implementing security measures across your AWS resources, you should use a holistic approach that incorporates controls across multiple areas. In the Cloud Adoption Framework (CAF) Security perspective whitepaper, we define these controls across four categories. Directive controls. Establish the […]

New Security Whitepaper Now Available: Use AWS WAF to Mitigate OWASP’s Top 10 Web Application Vulnerabilities
Today, we released a new security whitepaper: Use AWS WAF to Mitigate OWASP’s Top 10 Web Application Vulnerabilities. This whitepaper describes how you can use AWS WAF, a web application firewall, to address the top application security flaws as named by the Open Web Application Security Project (OWASP). Using AWS WAF, you can write rules to […]

How to Use AWS CloudFormation to Automate Your AWS WAF Configuration with Example Rules and Match Conditions
Note from July 4, 2017: The solution in this post has been integrated into AWS WAF Security Automations, and AWS maintains up-to-date solution code in the companion GitHub repository. AWS WAF is a web application firewall that integrates closely with Amazon CloudFront (AWS’s content delivery network [CDN]). AWS WAF gives you control to allow or block […]

How to Import IP Address Reputation Lists to Automatically Update AWS WAF IP Blacklists
Note from July 3, 2017: The solution in this post has been integrated into AWS WAF Security Automations, and AWS maintains up-to-date solution code in the companion GitHub repository. You can use AWS WAF (a web application firewall) to help protect your web applications from exploits that originate from groups of IP addresses that are known […]

How to Reduce Security Threats and Operating Costs Using AWS WAF and Amazon CloudFront
Note from July 3, 2017: The solution in this post has been integrated into AWS WAF Security Automations, and AWS maintains up-to-date solution code in the companion GitHub repository. Some Internet operations trust that clients are “well behaved.” As an operator of a publicly accessible web application, for example, you have to trust that the clients […]

How to Use AWS WAF to Block IP Addresses That Generate Bad Requests
Note from July 3, 2017: The solution in this post has been integrated into AWS WAF Security Automations, and AWS maintains up-to-date solution code in the companion GitHub repository. Internet-facing web applications are frequently scanned and probed by various sources, sometimes for good and other times to identify weaknesses. It takes some sleuthing to determine the […]